0:00 / 0:30

OpenIY MDM

Devices Reimagined


Driving Compliance to Devices IT, OT, IoT & IIoT solutions to be Resilient, Reliable, Scalable, and Secure

  • Identify
  • Enforce
  • Verify
  • Evidence
A professional at a laptop, with a phone beside it linked by a single orange arc
User identity + device identityThe person at the keyboard and the device in the session are one identity. OpenIY records both.

The identity gap

Credentials prove the person, not the device.


A completed sign-in shows that someone knew the password and the second factor. It does not show that the device is owned, patched, encrypted, or known to the organisation.

In banking, capital markets, insurance, and healthcare, that missing half is what auditors and supervisors ask about. ISO/IEC 27001, the NIST frameworks, PCI DSS, SOC 2, and the EU’s Digital Operational Resilience Act (DORA) all expect an organisation to know which endpoints reach sensitive data. National regulators such as the RBI, FCA, MAS, and SEC expect the same.

The session is allowed to touch customer data. The device in the session is still a blank.

OpenIY records device identity beside the user, and keeps the evidence.

A signed-in user beside a device that is still unknownUSERr.mehtaMFA okDEVICE?owner unknownpatch unknown

Frameworks

  • ISO/IEC 27001
  • NIST
  • PCI DSS
  • SOC 2
  • DORA

Supervisors

  • RBI
  • FCA
  • MAS
  • SEC

Platform

Identify. Enforce. Verify. Evidence.


Corporate user identity is user identity plus device identity. Our Proven 8-Step Framework for Scalable Endpoint Management The eight steps sit under those four acts.

  1. Identify

    Name every device, who holds it, and the risk it carries.

    1. 01

      Assess & Discover

      Auto-discover all devices (IT, OT, IoT, IIoT), classify by type, ownership, and risk posture.

      Complete visibility across endpoints and shadow IT elimination.

    2. 02

      Plan & Architect

      Define policies, compliance needs, app deployment strategies, and user roles.

      Customized MDM/UEM architecture aligned to org workflows.

  2. Enforce

    Put policy on the device at enrollment and keep it there.

    1. 03

      Provision & Enroll

      Onboard devices via zero-touch or QR enrollment, assign policies and profiles automatically.

      Fast, standardized provisioning across user/device types.

    2. 04

      Secure & Configure

      Enforce security baselines: DLP, encryption, VPN, firewall, kiosk/ single/ multi-app modes.

      Devices are policy-compliant, secure, and hardened from day one.

    3. 05

      Deploy & Control

      Push apps, updates, and content over-the-air; remote lock/ wipe; manage assets centrally.

      Centralized control with minimal user intervention.

  3. Verify

    Check posture continuously, and support the device when it drifts.

    1. 06

      Monitor & Support

      Real-time tracking of health, usage, compliance, and security posture. Provide remote support.

      Proactive management, incident resolution, and policy updates.

  4. Evidence

    Keep the record an auditor can read, through retirement.

    1. 07

      Optimize & Report

      Run lifecycle analytics, license audits, usage optimization, and compliance reporting.

      Continuous improvement + audit readiness.

    2. 08

      Retire & Recycle

      Offboard devices securely, wipe data, update inventory, and prepare for reuse/replacement.

      Secure deprovisioning and lifecycle closure.

Capabilities

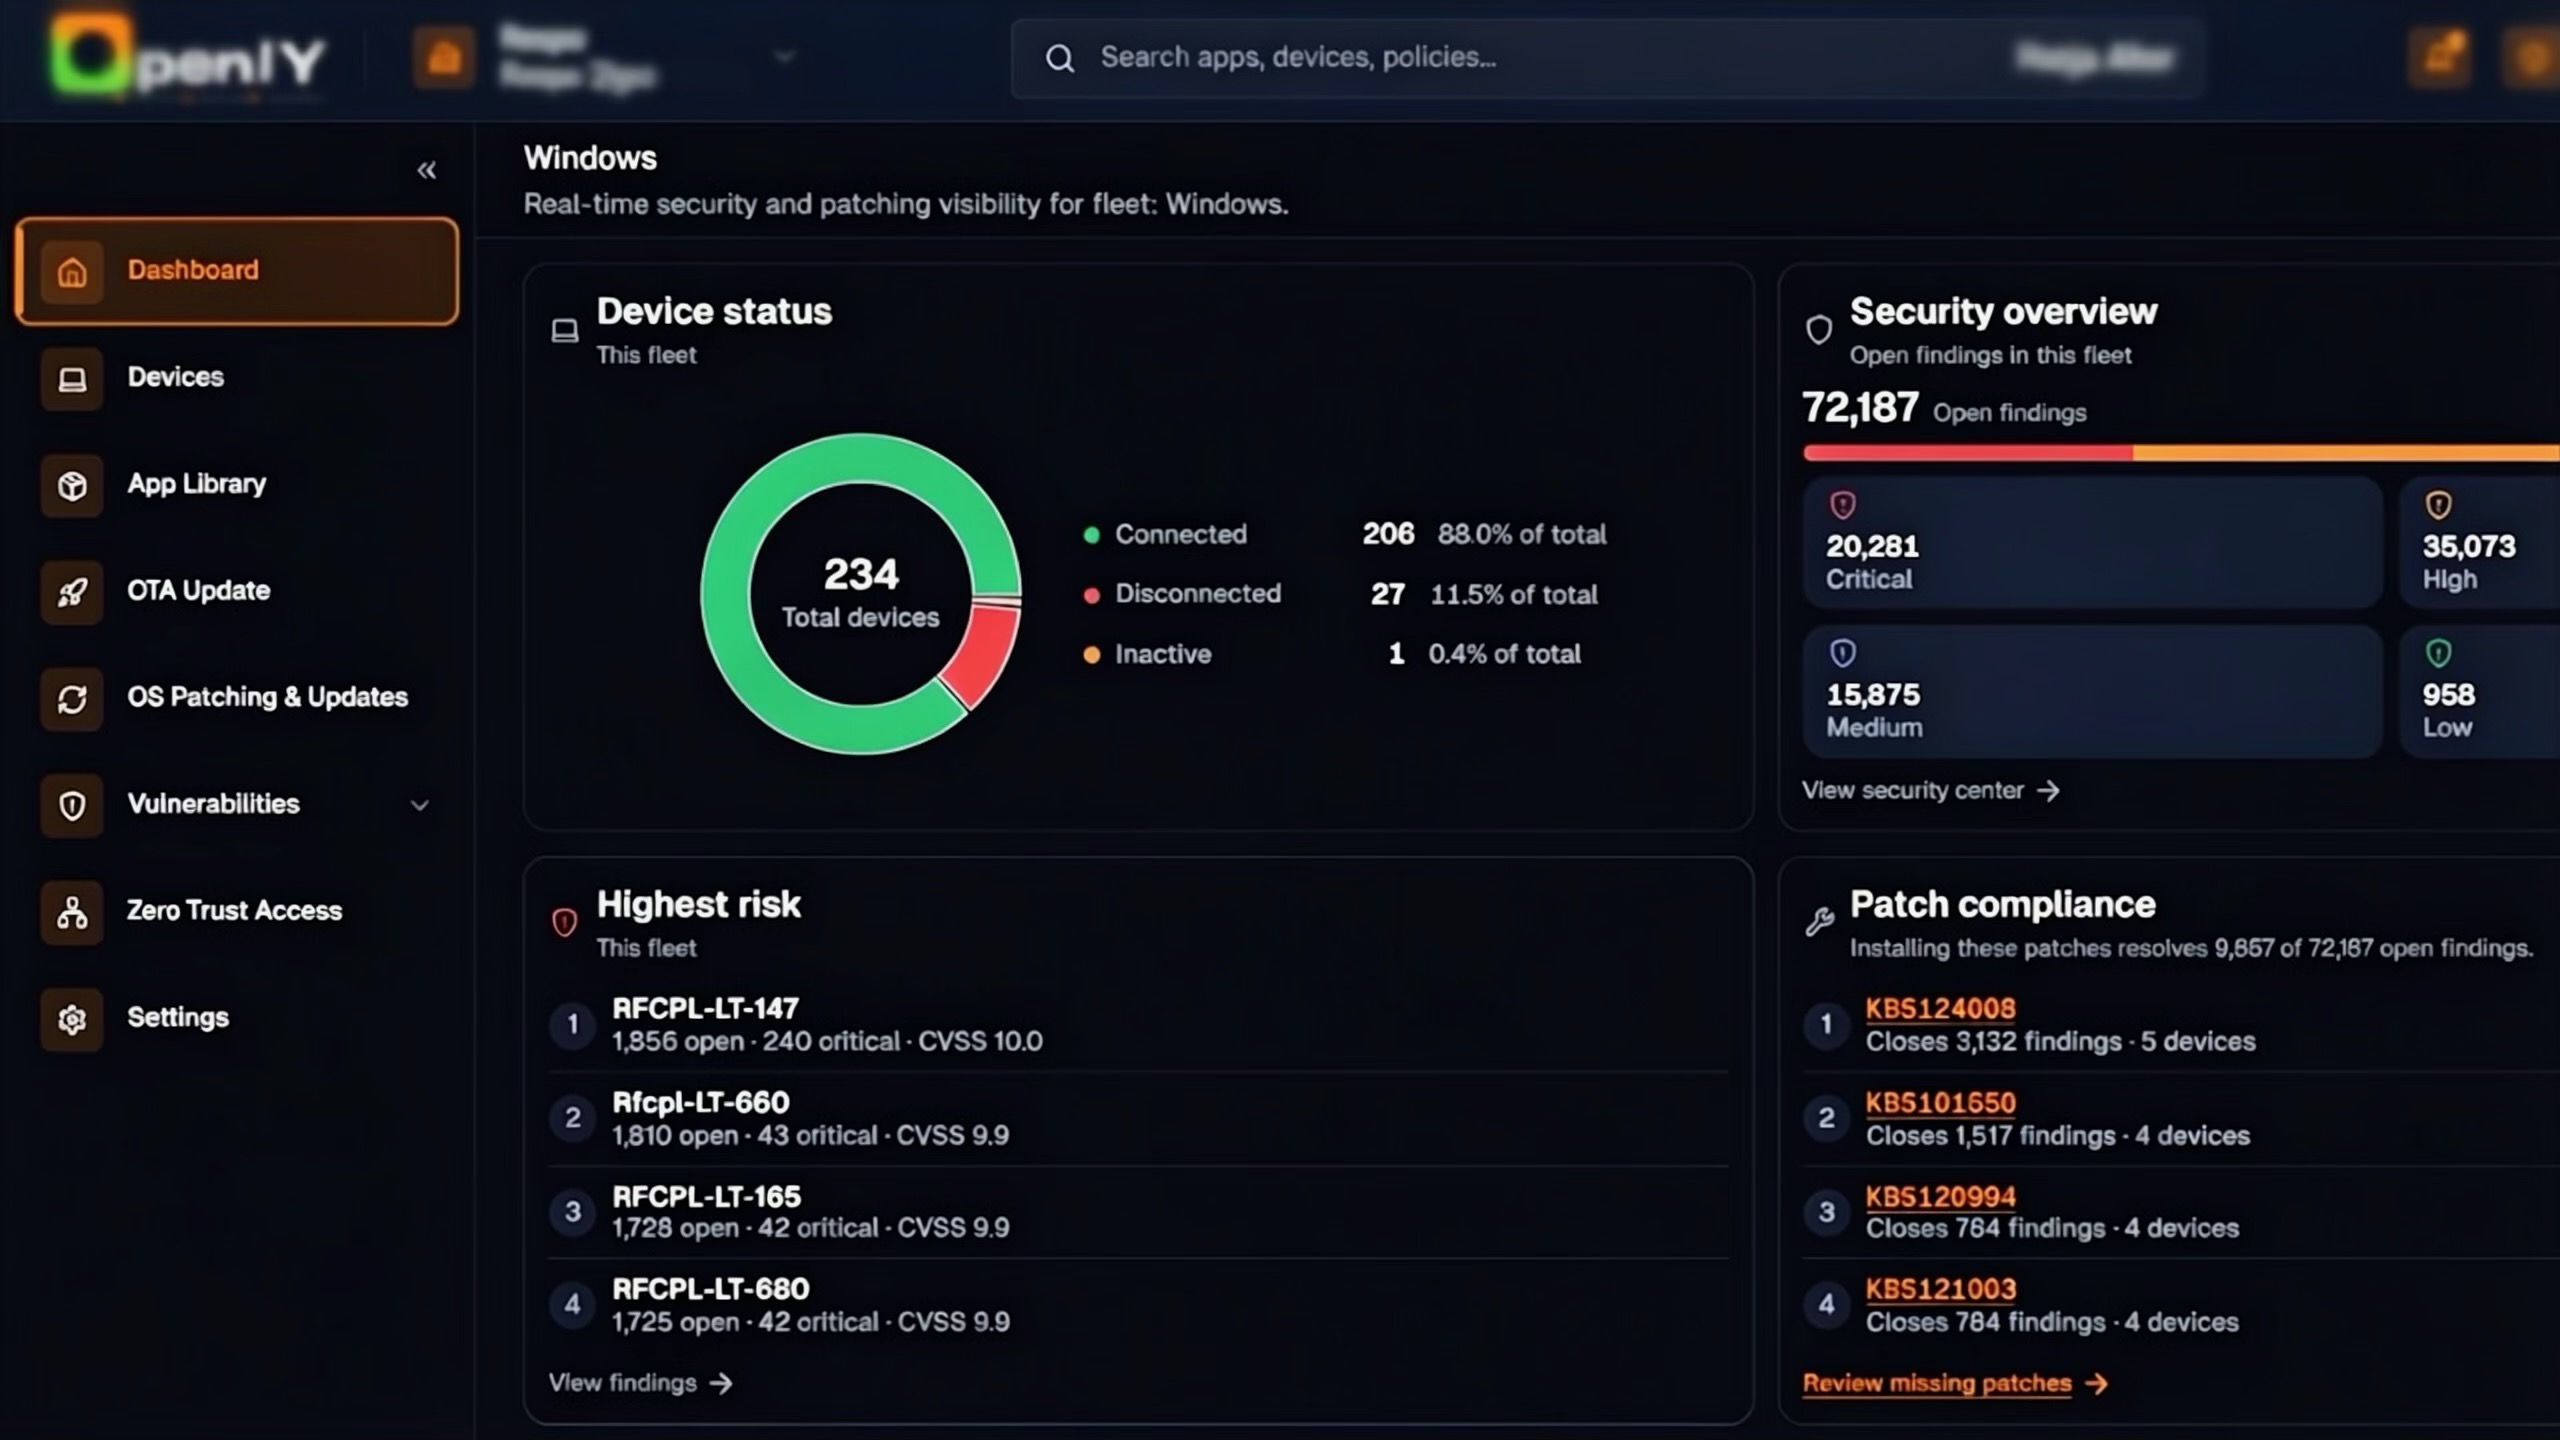
What the console holds


The OpenIY MDM console showing fleet posture, recent policy actions and a device record
  • Deterministic OTA

    An update can be started, stopped, paused, resumed, or restarted. The operator sets the window. The device does not move ahead of the plan.

  • SBOM and vulnerability assessment

    OpenIY keeps a software bill of materials for the device and assesses known vulnerabilities against it, so teams can show the inventory the EU Cyber Resilience Act expects connected products to account for.

  • Device posture and compliance-based access

    Access follows the device, not only the account. A session proceeds when posture matches the policy in force.

Coverage

Platforms under management


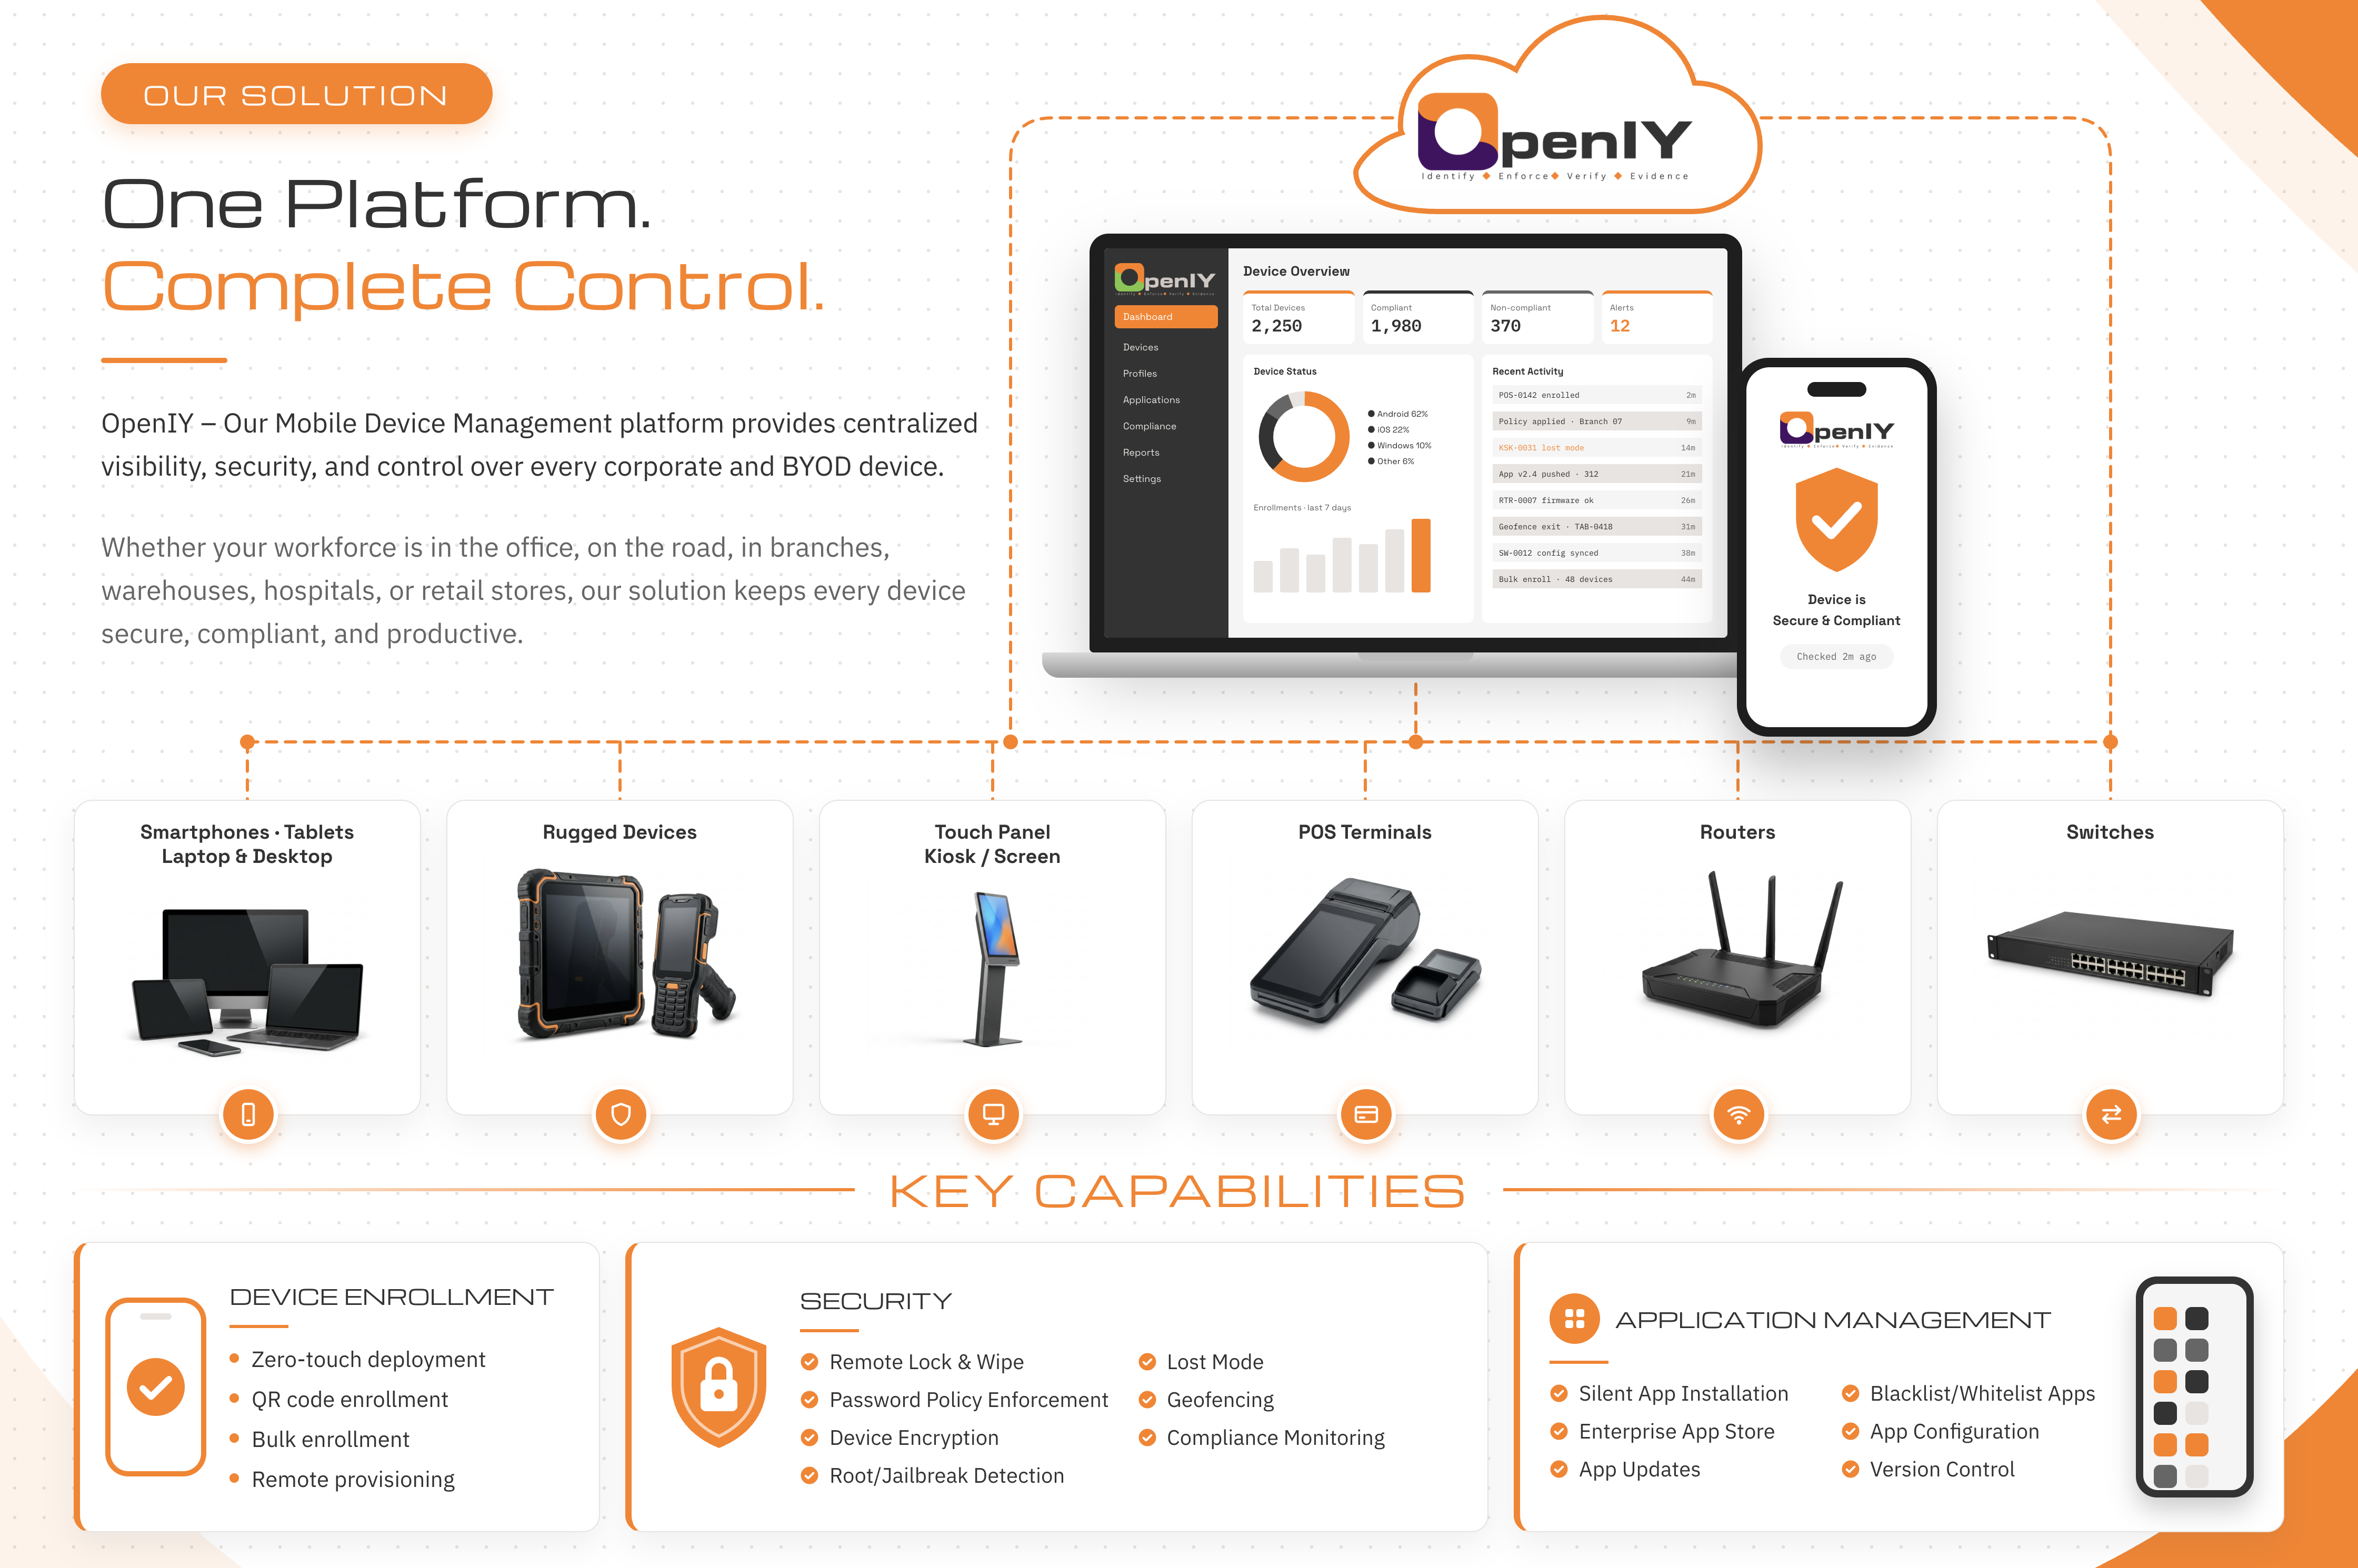
OpenIY MDM manages Windows, Linux, macOS, Android, iOS/iPadOS, OpenWRT, and RTOS from one console.

OpenIY MDM covering phones, rugged devices, kiosks, POS, routers and switches from one console
Platform coverage for OpenIY MDM.
PlatformSegmentIn the console
WindowsIT endpointCorporate and personal devices
LinuxIT and OTServers, appliances, and industrial hosts
macOSIT endpointApple Business Manager APIs, as a peer
AndroidMobile and IoTWork profile, kiosk, and dedicated devices
iOS / iPadOSMobileApple Business Manager APIs, as a peer
OpenWRTNetwork and IoTRouters and gateways
RTOSOT and IIoTConstrained devices

Deploy

Cloud, hybrid, or on premises


Devices check in to the OpenIY cloud console, which returns policy and stores evidenceDevicesIT, OT, IoT, IIoTOpenIY cloudPolicy and evidenceFleet record

The console and the evidence store run in OpenIY's cloud. Devices check in. Policy is decided there and delivered to the endpoint.

Apple Business Manager

OpenIY and Apple Business Manager exchange APIs as peer systemsApple BusinessManagerAPIsOpenIY

OpenIY consumes Apple Business Manager APIs directly, as a peer system.

Firewalls

Eleven firewall platforms receive policy from OpenIY0102030405060708091011OpenIY policy11

Firewall policy is supported across eleven platforms.

Proof

~15,000

Devices across three NBFCs


Under management on OpenIY MDM.

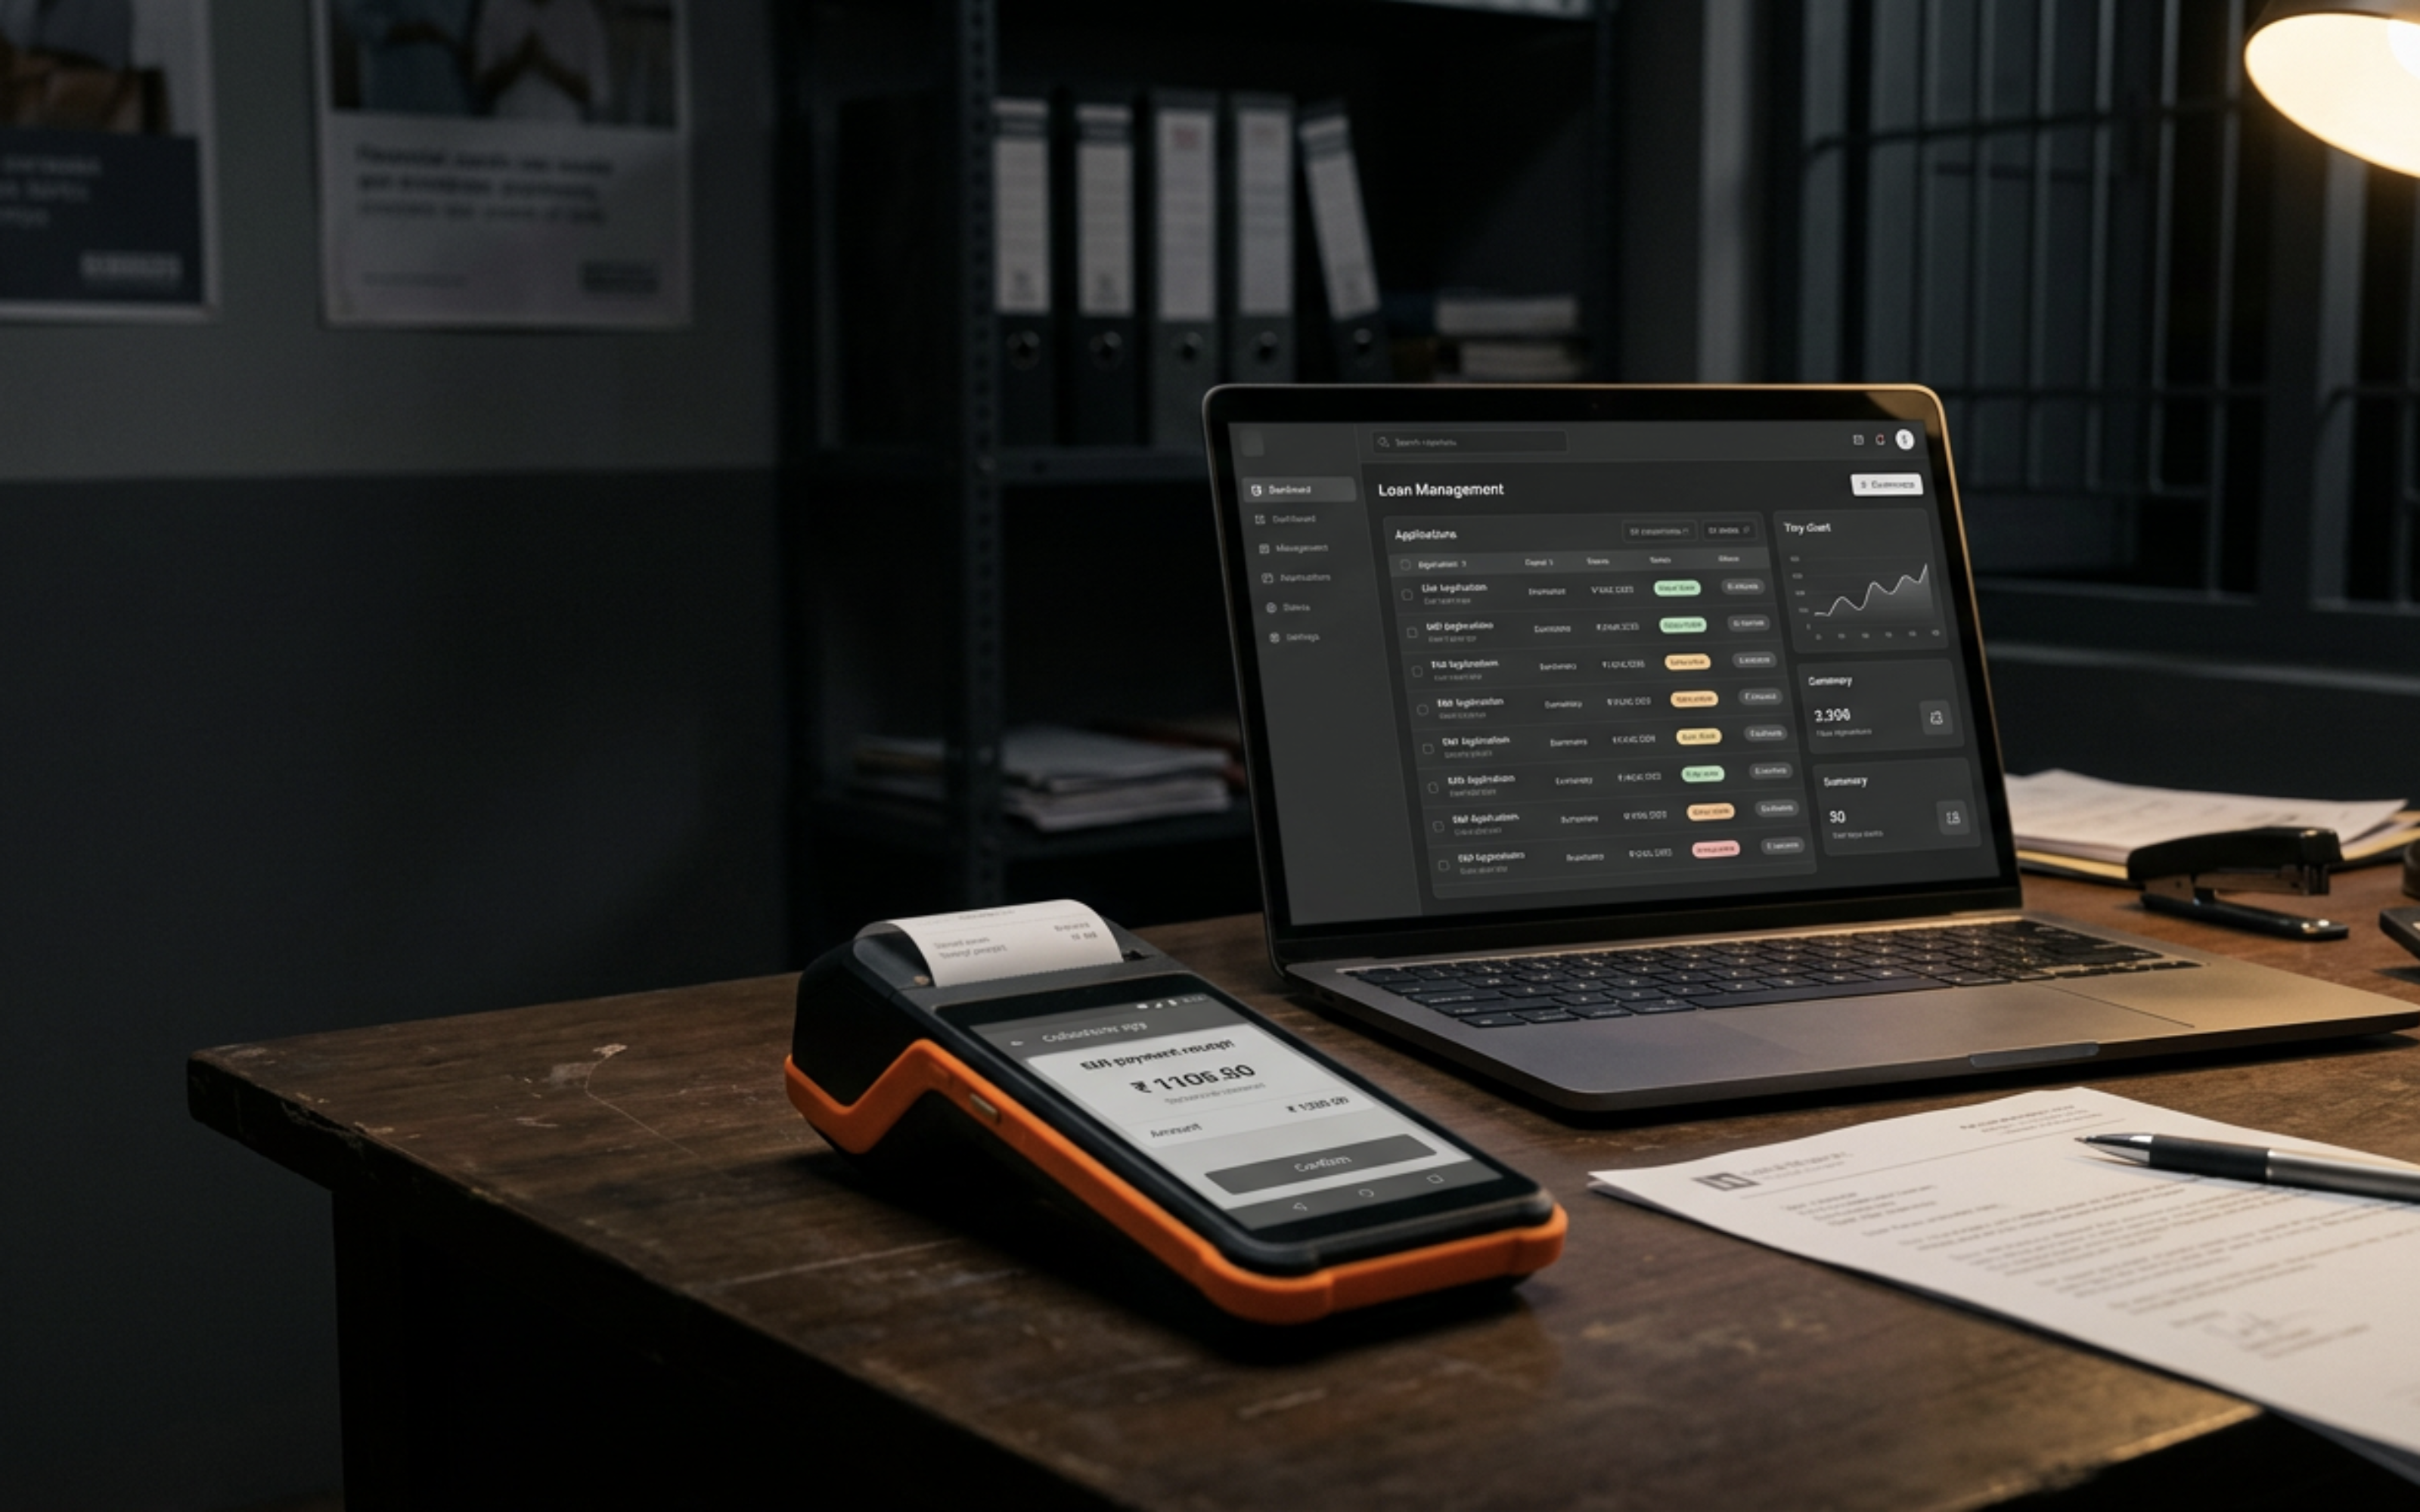
A collections handset and a loan-management laptop on a lending desk

What Our Clients are Saying

  • I have had the privilege of working with Mekosha Technologies, led by the exceptional Smideep and Ramnath, for a long time. Their team consistently demonstrates creativity, professionalism, and a deep commitment to excellence. Mekosha's expertise in IT infrastructure, security solutions, and compliance is unparalleled. They approach every project with integrity, ensuring innovative and reliable solutions tailored to client needs. Above all, their trustworthiness and dedication set them apart as partners. Whether it's managing complex deployments or delivering bespoke IT solutions, Mekosha Technologies is a name I wholeheartedly recommend for any organization looking for resilient and secure IT services.

    Panos LeledakisIFA Academy

  • Mekosha has made a promising start to our VAPT engagement, demonstrating a thorough understanding of our security requirements. Their initial approach and communication have been professional and reassuring. We look forward to seeing the value they bring to our security posture.

    JacobShivani Scientific

  • Mekosha Technologies has been an invaluable partner in strengthening our IT infrastructure. Their expert guidance and cost-effective solutions have significantly improved our operational efficiency and IT security.

    SakshamGramSakshamGram

Why Choose Us


  • Deep Cross-domain Expertise

    30+ years of expertise in IT and IoT, delivering secure, end-to-end solutions across diverse domains—from infrastructure to automation and analytics. Experienced in telecom, manufacturing, food and agri-tech, ed-tech, BPO/KPO and software sectors.

  • Compliance Without the Complexity

    Stay audit ready at all times with automated policy enforcement and real-time tracking. We help you align with frameworks like NIST, HIPAA, and ISO—without the manual overhead.

  • We believe in 'Zero Trust Model'

    At Mekosha, Zero Trust is our foundation. Every user, device, and action are continuously verified to ensure uncompromised security across your IT, IoT, and IIoT environments.

  • End-to-End Enterprise Security

    With native DLP, encryption, and IAM, we ensure proactive protection and policy-driven control across every endpoint enabling you to stay secure, compliant, and always in control.

  • All-in-one Platform

    A central control plane for complete visibility, action, and automation across your entire device ecosystem. We provide a single interface to manage devices across Windows, Linux, macOS, Android, iOS/iPadOS, OpenWRT, and RTOS.

  • Cross-Platform Reliability
  • Domain Specialists
  • Dedicated Care Partners

Industries

Where the fleet actually is


  • A collections handset and a loan-management laptop on a lending desk

    Fintech & NBFC

    Loan origination, collections, and branch devices sit on customer data. OpenIY binds each device to an owner, a posture, and a record the institution can show.

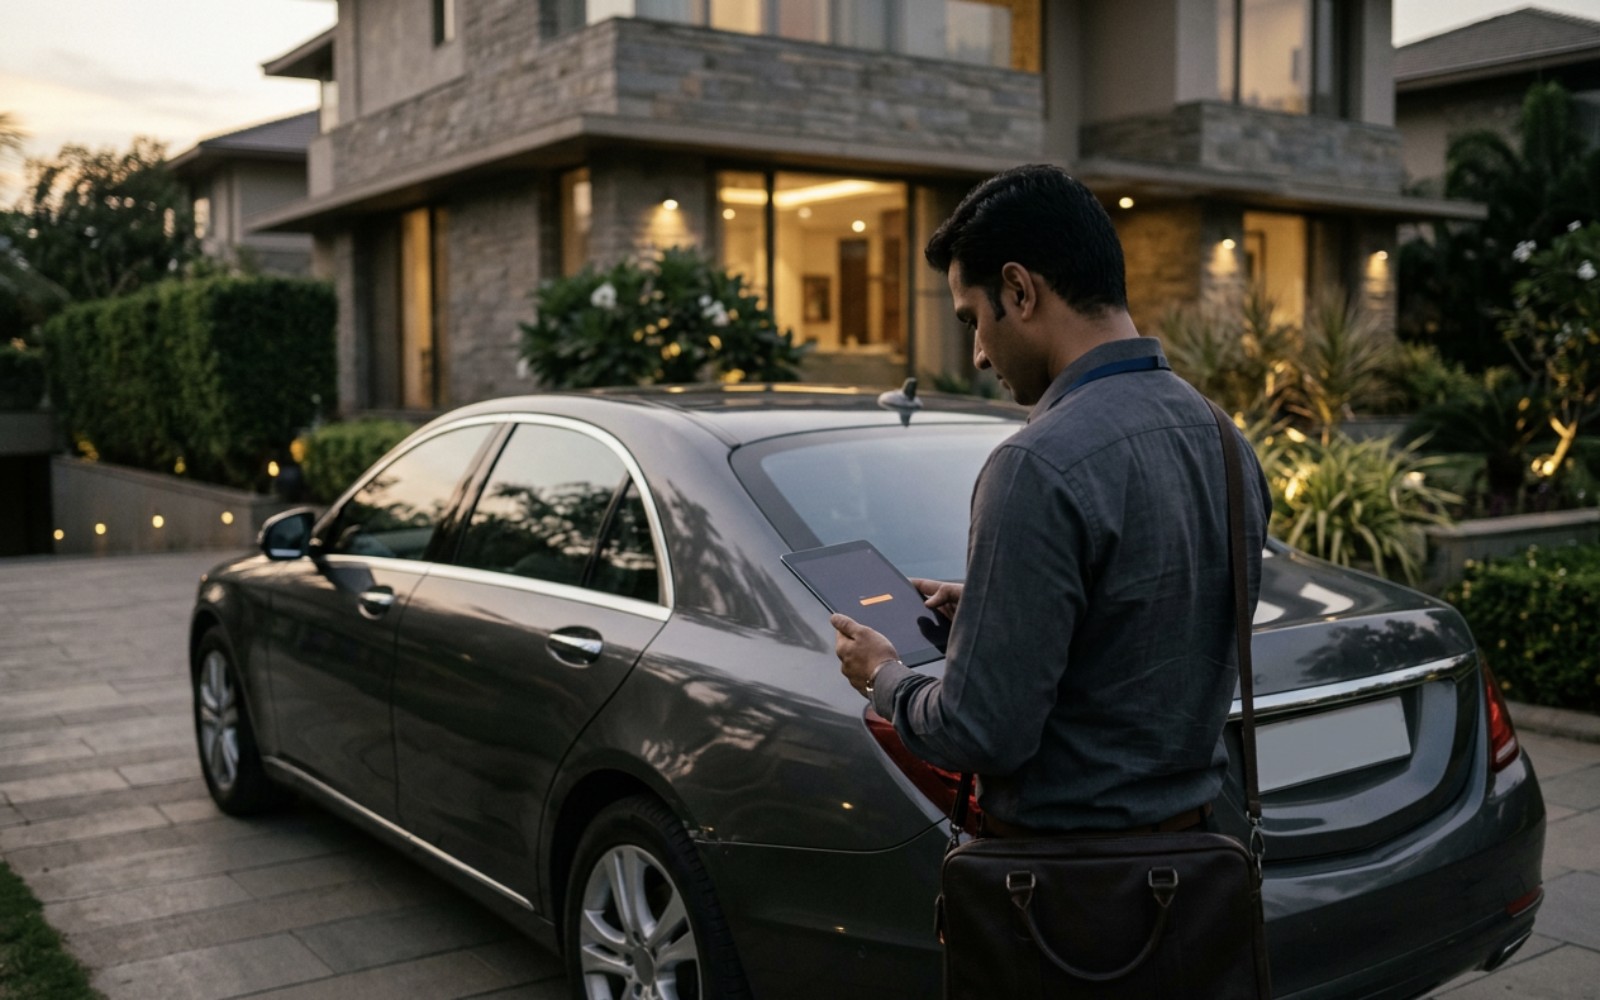
  • An insurance field agent with a tablet beside a car

    Insuretech

    Agent laptops and claims devices need the same account: who holds the device, what it runs, and whether it may open policyholder data.

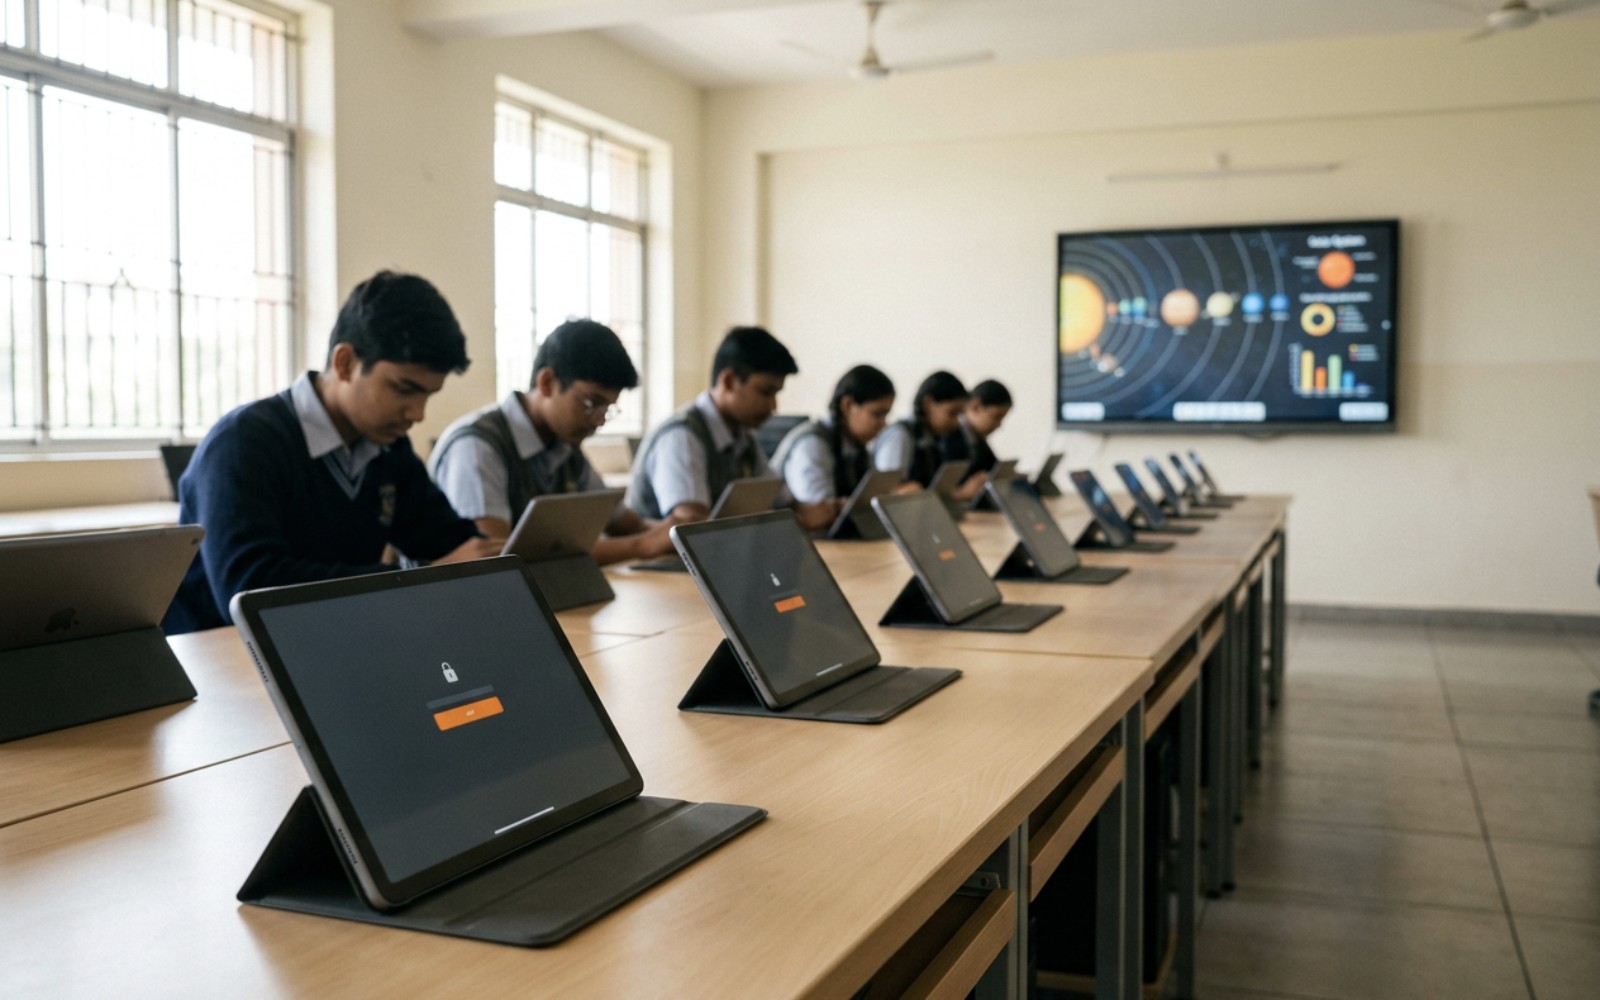
  • Exam devices in a school lab

    Edutech

    Shared labs, exam devices, and student endpoints stay on a known app set. Enrollment and lockdown are part of the school day.

  • Analysts at workstations on a knowledge-operations floor

    Knowledge & data ops

    Analyst endpoints move sensitive files all day. Sanctioned apps, restricted peripherals, and a software inventory keep the floor explainable.

  • Legal staff working with laptops and case files

    Legal

    Matter work stays on devices the firm can identify. Personal storage and unsanctioned apps stay outside the matter boundary.

  • A clinician using a shared tablet at a hospital station

    Medtech

    Clinical and frontline devices are shared and moved. Posture is checked before access, and the software on the device is known.

Company

Who we are


Mekosha Technologies delivers tailored infrastructure and security solutions that give you real-time visibility and control over devices, configurations, and compliance across your organization.

Meet Our Founders

  • Portrait of Smideep Nair

    Smideep Nair

    CEO & Co-Founder

    Smideep Nair is a technology strategist focused on redefining how organizations understand and leverage the devices that power modern industry. As CEO & Co-Founder of Mekosha Technologies Pvt. Ltd., he advocates a fundamental shift in industrial thinking — from viewing devices as operational necessities to treating them as intelligent, connected assets that form the foundation of future business models.

    With more than twenty years of experience spanning IT security, OT convergence, IoT, and Industrial IoT, his work sits at the intersection of secure infrastructure, asset intelligence, and digital transformation. He champions a security-first, compliance-aligned approach to innovation, enabling organizations to scale technology adoption without compromising resilience or governance — building a future where devices are not just managed, but orchestrated, analyzed, and leveraged as drivers of efficiency and growth.

  • Portrait of Ramnath Krishnan

    Ramnath Krishnan

    COO & Co-Founder

    Ramnath Krishnan brings over three decades of leadership and technical acumen to Mekosha. His career spans operations leadership in the chemical and cement industries, followed by two decades driving IT security, DevSecOps, and hardware and software configuration at Fortune 500 companies across telecommunications, computer hardware, and chip manufacturing.

    With extensive global experience across these domains, his focus at Mekosha is on building partnerships with MSME-sector companies to enable cost-effective adoption of IT security — making strategic, right-sized technology investments in an ever-evolving security landscape.

  • Portrait of Arun Ramnath

    Arun Ramnath

    CBO & Co-Founder

    Arun Ramnath is a digital transformation leader with over 20 years of experience in banking technology and RiskTech. As a co-founder of Mekosha, he leverages his global expertise to drive innovation in IoT, Mobile Device Management, and network security. Across his career he has transformed loss-making entities into profitable ventures and held multiple CXO positions focused on compliance, digital transformation, and disruptive technologies.

    His domain knowledge spans core banking systems, risk management, and regulatory compliance, with contributions to banks across APAC, Africa, the Middle East, and Southeast Asia. A sought-after educator, he has designed training programs for banking professionals and served as visiting faculty at prominent B-schools.

FAQ

Questions


OpenIY is built compliance-first, not device-first.

Traditional MDMs start with OS controls and later map them to compliance. OpenIY inverts this approach by:

Starting with regulatory and policy requirements

Translating them into device posture and enforcement profiles

Deploying controls in minutes across Android and iOS

This makes OpenIY particularly effective for regulated SMBs and growing enterprises that need immediate compliance alignment without MDM complexity

Insights

From the notebook


All posts

Contact

Request a demo


Tell us the fleet you run and the platforms in it. We will follow up at your work email.

Platforms

The OpenIY team in a support meeting
Request a demo